

Current CKA Exam Dumps [2026] Complete Linux Foundation Exam Smoothly
CKA Premium PDF & Test Engine Files with 85 Questions & Answers
The CKA Program Certification Exam consists of a set of performance-based tasks that candidates must complete within a given time frame. CKA exam covers a broad range of topics, including cluster architecture, installation and configuration, networking, storage, troubleshooting, and security. Candidates are expected to demonstrate their ability to perform tasks such as deploying applications, scaling and upgrading clusters, configuring network policies, troubleshooting node and cluster problems, and securing Kubernetes clusters.
NEW QUESTION # 25
You have a complex application with multiple services running in a Kubernetes cluster. Some services communicate with each other over the cluster network, while others need to access external services over the internet. You need to configure CoreDNS to handle both internal and external DNS resolution in a secure and efficient manner.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Configure CoreDNS for Internal DNS:
- Create a CoreDNS ConfigMap named 'coredns' with the following configuration:
-
2. Configure CoreDNS for External DNS: - If you need to resolve external domains, you can use CoreDNS's 'forward' plugin to forward requests to external DNS servers. You can configure 'forward' in the Corefile, or use environment variables to dynamically set the upstream servers.
3. Configure Services with External Names: - If you need to access external services, configure their services in Kubernetes with the 'externalName' field.
4. Use Secure DNS: - Enable DNS over TLS (DOT) or DNS over HTTPS (DOH) in your CoreDNS configuration to ensure secure DNS resolution.
5. Test DNS Resolution: - Test DNS resolution for internal and external domains using the 'nslookup command from pods in your cluster.
NEW QUESTION # 26
Install a kubernetes cluster with one master and one worker using kubeadm
- A. This is a straightforward question, you need to install kubernetes cluster using kubeadm with one master and one worker.
Refer : https://kubernetes.io/docs/setup/production-environment/tools/kubeadm/ - B. This is a straightforward question, you need to install kubernetes cluster using kubeadm with one master and one worker.
Installation is considered success once both master and worker
nodes become available.
Refer : https://kubernetes.io/docs/setup/production-environment/tools/kubeadm/
Answer: B
NEW QUESTION # 27
You are deploying a service in Kubernetes that needs to access a database service running in a different namespace. How can you configure NetworkPolicy to allow communication between these services across namespaces?
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1 . Create a NetworkPolicy in the service's namespace:
- Create a NetworkPolicy in the namespace of the service that needs to access the database.
- Code:
2. Ensure the Database Namespace has the Correct Label: - Ensure that the namespace where the database service is running has the label 'database: true'. 3. Apply the NetworkPolicy: - Apply the NetworkPolicy using 'kubectl apply -f networkpolicy.yaml'.
NEW QUESTION # 28
You are deploying a microservices application on Kubernetes where each service has its own dedicated namespace. You want to implement a robust network security policy that allows communication between specific services only. How can you achieve this using NetworkPolicies?
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Define Network Policies for Each Service:
- For each service, create a NetworkPolicy that defines the allowed ingress and egress traffic.
- Example for service "service-A":
2. Apply Network Policies: - Apply the NetworkPolicies to the respective namespaces using 'kubectl apply -f networkpolicy.yaml'
NEW QUESTION # 29
Set the node named ek8s-node-1 as unavailable and reschedule all the pods running on it.
Answer:
Explanation:
See the solution below.
Explanation
solution
F:\Work\Data Entry Work\Data Entry\20200827\CKA\19 B.JPG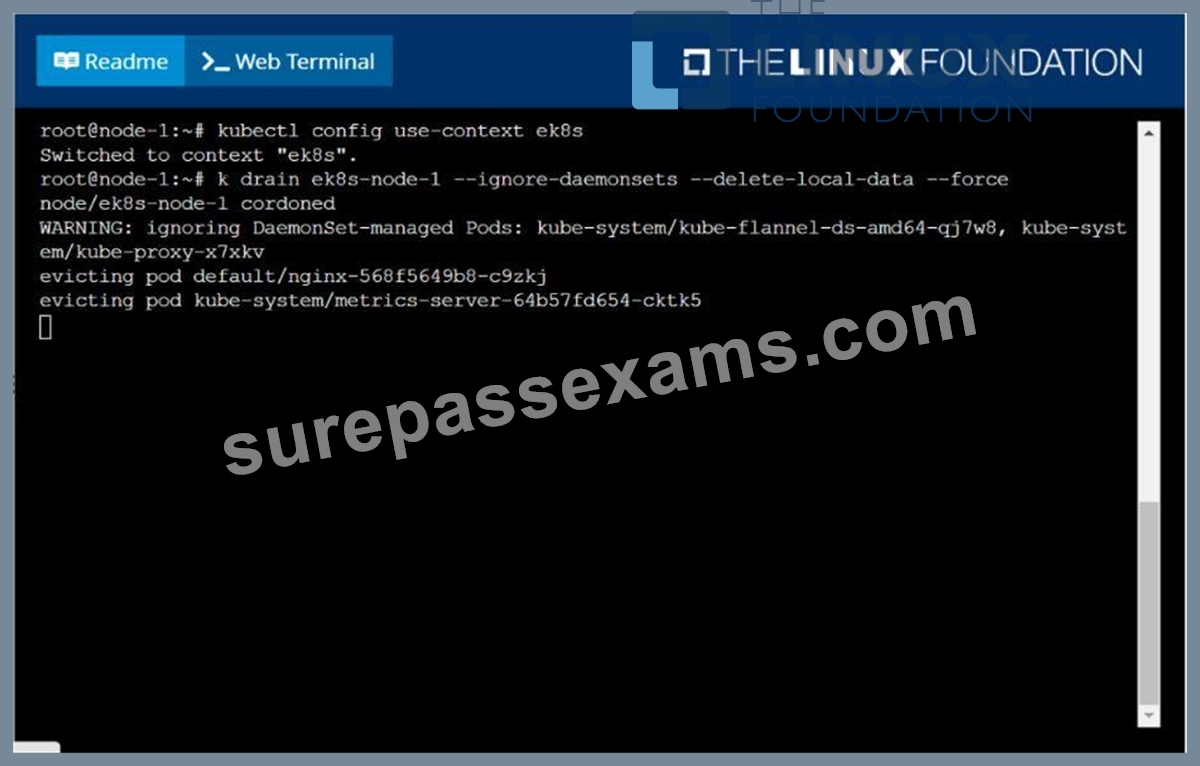
NEW QUESTION # 30
For this item, you will have to ssh to the nodes ik8s-master-0 and ik8s-node-0 and complete all tasks on these nodes. Ensure that you return to the base node (hostname: node-1) when you have completed this item.
Context
As an administrator of a small development team, you have been asked to set up a Kubernetes cluster to test the viability of a new application.
Task You must use kubeadm to perform this task. Any kubeadm invocations will require the use of the --ignore-preflight-errors=all option.
Configure the node ik8s-master-O as a master node. .
Join the node ik8s-node-o to the cluster.
Answer:
Explanation:
solution
You must use the kubeadm configuration file located at /etc/kubeadm.conf when initializing your cluster.
You may use any CNI plugin to complete this task, but if you don't have your favourite CNI plugin's manifest URL at hand, Calico is one popular option: https://docs.projectcalico.org/v3.14/manifests/calico.yaml Docker is already installed on both nodes and apt has been configured so that you can install the required tools.
NEW QUESTION # 31
List all the pods that are serviced by the service "webservice" and copy the output in /opt/$USER/webservice.targets Note: You need to list the endpoints
Answer:
Explanation:
kubectl descrive svc webservice | grep -i "Endpoints" > /opt/$USER/webservice.targets kubectl get endpoints webservice > /opt/$USER/webservice.targets
NEW QUESTION # 32
Create a deployment spec file thatwill:
* Launch 7 replicas of thenginxImage with the labelapp_runtime_stage=dev
* deployment name:kual00201
Save a copy of this spec file to/opt/KUAL00201/spec_deployment.yaml
(or/opt/KUAL00201/spec_deployment.json).
When you are done, clean up (delete)any new Kubernetes API object thatyou produced during this task.
Answer:
Explanation:
See the solution below.
Explanation
solution

NEW QUESTION # 33
Create a pod with image nginx called nginx and allow traffic on port 80 See the solution below.
Answer:
Explanation:
kubectl run nginx --image=nginx --restart=Never --port=80
NEW QUESTION # 34
Score: 4%
Context
You have been asked to create a new ClusterRole for a deployment pipeline and bind it to a specific ServiceAccount scoped to a specific namespace.
Task
Create a new ClusterRole named deployment-clusterrole, which only allows to create the following resource types:
* Deployment
* StatefulSet
* DaemonSet
Create a new ServiceAccount named cicd-token in the existing namespace app-team1.
Bind the new ClusterRole deployment-clusterrole lo the new ServiceAccount cicd-token , limited to the namespace app-team1.
Answer:
Explanation:
See the solution below.
Explanation
Solution:
Task should be complete on node -1 master, 2 worker for this connect use command
[student@node-1] > ssh k8s
kubectl create clusterrole deployment-clusterrole --verb=create
--resource=deployments,statefulsets,daemonsets
kubectl create serviceaccount cicd-token --namespace=app-team1
kubectl create rolebinding deployment-clusterrole --clusterrole=deployment-clusterrole
--serviceaccount=default:cicd-token --namespace=app-team1
NEW QUESTION # 35
You have a Deployment named 'wordpress-deployment' running a WordPress application with two pods. The WordPress application needs to access a shared secret key stored in a Secret named 'wordpress- secret'. How do you ensure the secret key is securely mounted and available to both pods?
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create the Secret:
- Create a Secret named 'wordpress-secret' containing the shared secret key. Use 'kubectl create secret generic' with the '-from-literal' flag to create a generic Secret:
kubectl create secret generic wordpress-secret --from-literal=wordpress-secret="your secret_key"
2. Configure the Deployment:
- Modify the 'wordpress-deployment' Deployment to mount the 'wordpress-secref Secret as a volume in the Pod template. Use 'volumeMounts' to specify the mount path and 'volumes' to define the Secret as a volume source:
3. Apply the Changes: - Apply the modified Deployment YAML using 'kubectl apply -f wordpress-deployment.yaml'. 4. Verify the Secret Mount: - Use 'kubectl exec' to access a pod in the 'wordpress-deployment' and verify that the Secret is mounted at the specified path (e.g., 'Ivar/run/secrets/wordpress'). 5. Access the Secret Key: - Within the WordPress application's code, access the secret key from the mounted path.
NEW QUESTION # 36
An Administrator is configuring Authentication Enforcement and they would like to create an exemption rule to exempt a specific group from authentication. Which authentication enforcement object should they select?
- A. default-no-captive-port
- B. default-web-form
- C. default-authentication-bypass
- D. default-browser-challenge
Answer: A
NEW QUESTION # 37
You are tasked with setting up fine-grained access control for a Kubernetes cluster running a microservices application. You need to ensure that developers can only access the resources related to their specific microservices while preventing them from accessing or modifying other services' resources. Define RBAC roles and permissions to achieve this, including details of the resources, verbs, and namespaces involved. Consider the following:
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Specify the YAML configurations for roles, role bindings, and service accounts to enable the required access control, ensuring developers only have access to their respective microservice's resources within their assigned namespaces. Solution (Step by Step) : 1. Define Roles:
2. Create Service Accounts: apiVersion: vl kind: ServiceAccount metadata: name: order-service-sa namespace: order-service-ns -- apiVersion: vl kind: ServiceAccount metadata: name: payment-service-sa namespace: payment-service-ns -- apiVersion: vl kind: ServiceAccount metadata: name: inventory-service-sa namespace: inventory-service-ns 3. Bind Roles to Service Accounts: -- apiVersion: rbac.authorization.k8s.io/v1 kind: RoleBinding metadata: name: order-service-dev-binding namespace: order-service-ns roleRef: apiGroup: rbac.authorization.k8s.io kind: Role name: order-service-dev subjects: - kind: ServiceAccount name: order-service-sa namespace: order-service-ns -- apiVersion: rbac.authorization.k8s.io/v1 kind: RoleBinding metadata: name: payment-service-dev-binding namespace: payment-service-ns roleRef: apiGroup: rbac.authorization.k8s.io kind: Role name: payment-service-dev subjects: - kind: ServiceAccount name: payment-service-sa namespace: payment-service-ns -- apiVersion: rbac.authorization.k8s.io/v1 kind: RoleBinding metadata: name: inventory-service-dev-binding namespace: inventory-service-ns roleRef: apiGroup: rbac.authorization.k8s.io kind: Role name: inventory-service-dev subjects: - kind: ServiceAccount name: inventory-service-sa namespace: inventory-service-ns 4. Assign Service Accounts to Users: This step requires external authentication mechanisms like OIDC or LDAP. Assuming you have these mechanisms set up, you can associate the service accounts with specific users ('[email protected]' , '[email protected]', and '[email protected]') using the configured authentication provider. Roles: Define the specific permissions for each microservice developer within their respective namespaces. The roles allow developers to access resources like Pods, Deployments, Services, ConfigMaps, and Secrets related to their assigned microservice. Service Accounts: Service accounts are created in each namespace for each microservice, representing the identity of the developer group. Role Bindings: Role bindings connect the defined roles with the service accounts, granting the associated permissions. User Association: This step connects the service accounts with individual developers through external authentication mechanisms, enabling them to utilize the assigned permissions. By following these steps, you ensure that developers can only access and manage resources associated with their respective microservices within their assigned namespaces. This fine-grained access control policy effectively restricts access and prevents developers from interfering with other microservices or resources. ,
NEW QUESTION # 38
Clean the cluster by deleting deployment and hpa you just created
Answer:
Explanation:
kubectl delete deploy webapp kubectl delete hpa webapp
NEW QUESTION # 39
Watch the job that runs 10 times one by one and verify 10 pods are created and delete those after it's completed
Answer:
Explanation:
kubectl get job -w kubectl get po kubectl delete job hello-job
NEW QUESTION # 40
......
The CKA exam is designed to test an individual's ability to perform real-world tasks in a Kubernetes environment. CKA exam is conducted online and consists of a set of performance-based tasks that need to be completed within a given time frame. CKA exam covers a range of topics such as Kubernetes architecture, installation and configuration, networking, storage, security, and troubleshooting. CKA exam is challenging and requires a high level of expertise in Kubernetes administration. However, passing the exam is a testament to an individual's skills and knowledge in Kubernetes and can lead to better job opportunities and career growth in the industry.
How much CNCF CKA Certification Exam Cost and Details
- Retake Exam: Free
- No. of Questions: 17 Questions
- Passing score: 66% or higher
- Length of Exam: 120 min
- Examination Name: CNCF CKA Certification
- Examination Fees: $375 USD
CKA Premium Files Practice Valid Exam Dumps Question: https://dumpsninja.surepassexams.com/CKA-exam-bootcamp.html